GitLab 19.4 Brings AI Agents Into Delivery Operations With Human Approval Defaults
Public beta
GitLab 19.4 introduces MCP server tools in public beta under the GitLab Duo Agent Platform.
Approval split
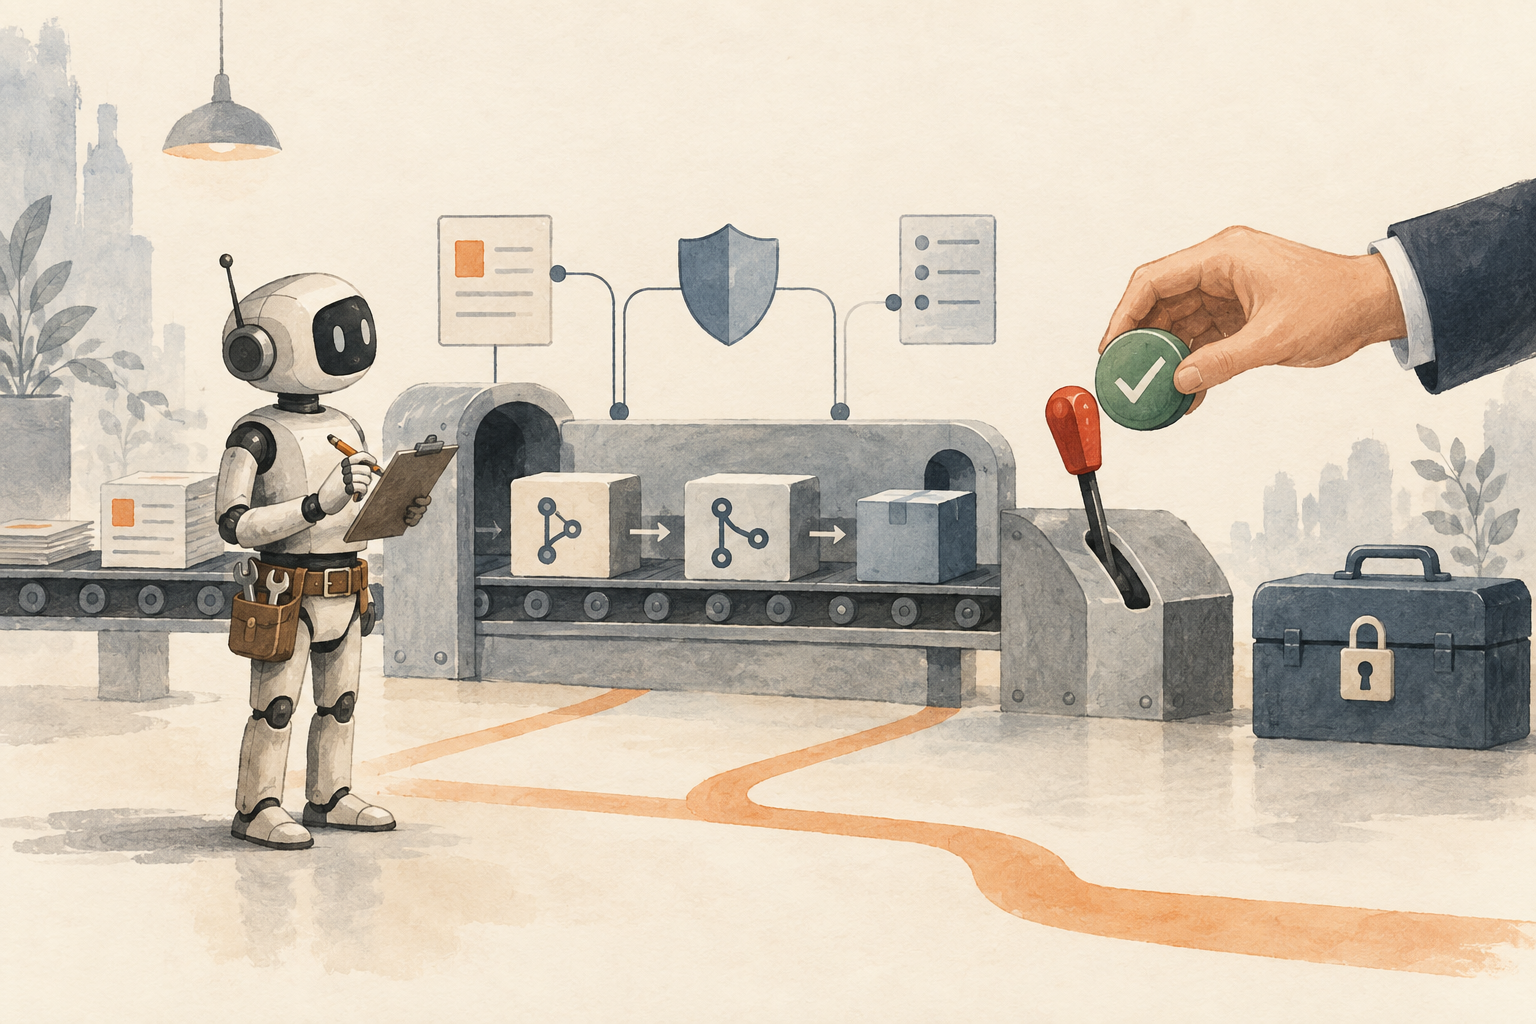
Read-only tools default to Always Allow, while write and delete actions default to Always Ask for human approval.
Delivery scope
The tools cover CI/CD, merge requests, repositories, work items, projects, users and vulnerability workflows.
GitLab 19.4 extends AI agents beyond code assistance and into software-delivery operations, adding public-beta Model Context Protocol server tools that can trigger CI/CD pipelines, inspect failed jobs, manage merge requests, update work items and triage vulnerabilities under existing GitLab Duo governance controls.12
The key control is the default permission split: read-only MCP tools are set to “Always Allow,” while write and delete tools default to “Always Ask,” requiring human confirmation before an agent changes project state.124 For DevSecOps platform teams, per-tool approval and auditability become the practical control plane for agentic software development.
The release, published Sept. 17, adds new MCP tool bundles in public beta under the GitLab Duo Agent Platform. The tools allow external clients, including AI coding environments, to call GitLab functions through a standardized interface.15 Coverage spans CI/CD pipelines, merge requests, repositories, work items, projects, users and vulnerability-management workflows, according to multiple reports on the 19.4 release.246
The new tools move agents from suggestion-only workflows into operational tasks that historically required a developer, maintainer or security engineer to work inside GitLab. Reported CI/CD capabilities include running, retrying or canceling pipelines and retrieving job logs so an agent can investigate a failed build.1 Merge-request tools cover creating or updating MRs, adding review comments and, where permitted, accepting merge requests.13
Work item tools allow agents to retrieve, list and update issues, epics, tasks and incidents. Vulnerability tools can support triage actions such as dismissing, confirming or changing severity, subject to the same governance model.23 Repository tools also expand the operational surface by enabling branch, commit and fork workflows.13
The result is a broader automation surface across the DevSecOps lifecycle. Instead of asking an assistant for a patch and then manually moving through pipelines, reviews and security queues, teams can test whether agents can help coordinate more of the delivery process from a single MCP-connected client.5
GitLab’s default policy split is designed to preserve speed for low-risk context gathering while keeping a human checkpoint for state-changing operations. Read-only actions, such as listing projects or inspecting job output, can proceed without repeated prompts. Actions that write, modify, merge, dismiss or delete require approval by default.124
That distinction matters because delivery systems are not just code editors. A pipeline cancellation, vulnerability dismissal or merge action can affect production readiness, compliance evidence and release timing. By making write and delete operations “Always Ask” by default, GitLab treats agentic actions as governed platform operations rather than background assistant behavior.23
Reports also note that agents operate through existing GitLab permissions. In practice, an external agent connected through the MCP path acts within the authority of the user and role it is operating under, rather than receiving a separate blanket permission set.3 Administrators can configure MCP tool governance from GitLab Duo settings at group and project scope, bringing external-agent controls into the same administrative surface used for Duo Agent Platform tools.16
For platform teams, the release shifts the governance question from “Should agents be allowed?” to “Which tools should be callable, by whom, and under what approval mode?” That is more granular than a simple enable-or-disable switch and maps more closely to how DevSecOps organizations already manage separation of duties.
The default split also creates a baseline operating pattern. Teams can allow agents to gather context freely, such as reading logs, checking MR status or listing work items, while keeping merges, vulnerability state changes, commits and destructive pipeline actions behind human approval. The same pattern can be tightened or loosened depending on repository criticality, environment, compliance obligations and team maturity.
The public-beta status is important. Platform teams evaluating the release should treat the tools as an opportunity to test policy design, approval workflows, user education and logging expectations before broader rollout. The key operational question is not only whether an agent can complete a delivery task, but whether the organization can explain who authorized each consequential action and why.
GitLab 19.4 arrives as AI development tooling moves from chat-based code generation toward goal-oriented and multi-step automation. Coverage of the release describes GitLab’s direction as a shift from reactive suggestions to autonomous task execution under enterprise controls.5 The same release also includes other agentic features, including the Duo CLI /goal command and broader model options, but the MCP governance model is the more immediate concern for platform owners managing risk across software delivery.24
The practical implication is that agent governance is becoming part of DevSecOps platform engineering. Approval defaults, per-tool policies, user-role boundaries and audit trails are likely to become as important as prompt quality or model selection when organizations connect AI agents to CI/CD, code review and security workflows.
For now, GitLab’s 19.4 approach sets a clear default: let agents read broadly enough to be useful, but require a person to approve actions that change the delivery system.12

Snap introduced Specs Intelligence, an AI service designed to carry personal context across its AR glasses, iPhone and Mac. The company is positioning the assistant as a proactive computing layer that can surface suggestions before users explicitly ask.

Hacktron researchers used Anthropic’s Claude to help build an exploit for an image-processing flaw, then chained it to an OpenAI sign-in-token issue to reach employee ChatGPT and Codex accounts. The incident shows how AI-assisted exploit development can compress the path from overlooked dependency bugs to privileged access in connected enterprise systems.

OpenAI introduced Astra for Law, a GPT-6 Astra configuration for U.S. legal work that pairs a dedicated legal search index with legal-domain instructions, privacy controls and partner workflows. The launch shows frontier AI vendors moving beyond general-purpose models toward vertical retrieval and workflow layers built for enterprise adoption.

Anthropic says Claude now leads 26% of its model R&D work, up from under 1% in February. The disclosure reframes recursive self-improvement as a measurable engineering process—but one still dependent on human supervision and largely self-assessed by the lab.
Model Context Protocol
MCP is a standard interface that lets AI agents connect to external tools, systems and data sources in a structured way.
Always Ask
A governance mode that requires a human approval step before an agent can perform a write or delete action.
GitLab Duo Agent Platform
GitLab’s platform layer for AI agent capabilities and governance across GitLab workflows.
Agentic software development
A development model in which AI agents perform multi-step tasks across tools, not just generate code suggestions.
Comments