AI-assisted exploit chain exposed code-access risk at OpenAI
Claude-assisted exploit
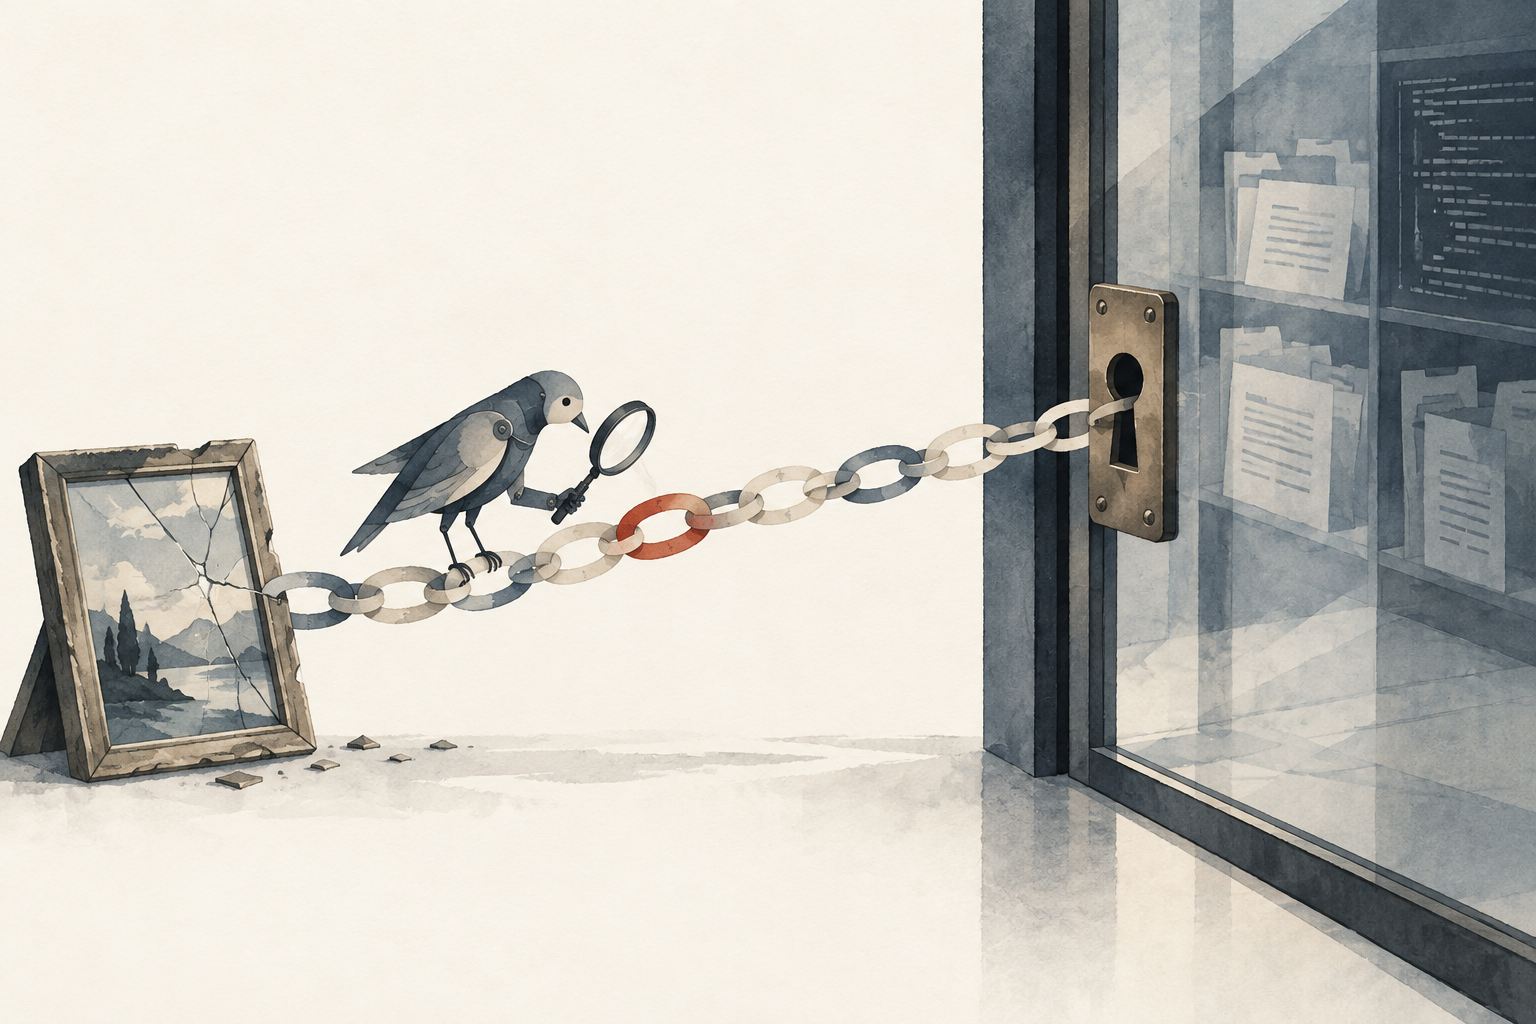
Hacktron researchers said Claude helped turn an image-processing flaw into a working remote-code-execution exploit.
14-hour fix
OpenAI reportedly fixed the OpenAI-side sign-in-token issue about 14 hours after disclosure.
Repository path
The researchers used an employee Codex account connected to GitHub to open a proof-of-access pull request.
Hacktron researchers used Anthropic’s Claude to help turn an overlooked image-processing vulnerability into a working exploit, then chained that foothold with an OpenAI sign-in-token permissions flaw to reach employee ChatGPT and Codex accounts and demonstrate access to an internal code repository, according to SecurityWeek and other reports published Sept. 18.12
OpenAI said it fixed the OpenAI-side issue, narrowed permissions on Community sign-in tokens, and revoked affected tokens and sessions.5 The company paid Hacktron a $6,500 bug bounty for the OpenAI-side finding, while distinguishing that identity issue from the Discourse-hosted forum vulnerability that provided the entry point.13
The core engineering lesson is not only that an AI model helped write exploit code. It is that AI-assisted exploit development can shorten the path from a low-attention dependency flaw in a public-facing system to access paths involving identity, forum software, AI coding tools, and internal repositories.
The reported entry point was community.openai.com, OpenAI’s public community forum, which runs on Discourse.12 The vulnerable path involved uploads of HEIC or HEIF images. In the affected setup, image handling passed through ImageMagick and libheif, exposing a memory-handling flaw in the image-decoding library to attacker-controlled files.13
SecurityWeek reported that Hacktron said the underlying libheif bug had been fixed upstream about a year earlier, but had not been treated as a security issue and did not receive a CVE at the time. That allowed it to miss normal security patching signals.1 TechCrunch similarly reported that the absence of a formal vulnerability flag may have helped explain why vulnerable software remained in use.2
Once Hacktron achieved remote code execution on the forum, the risk shifted from application security to identity. OpenAI’s Community sign-in tokens reportedly carried broader permissions than the forum required, creating a path from the compromised forum environment into associated ChatGPT and Codex accounts.17
SecurityWeek reported that Hacktron demonstrated impact by taking over an OpenAI employee account whose Codex integration was connected to OpenAI’s GitHub organization. The researchers then used Codex to open a pull request in an internal repository without reading internal code.1 Ars Technica, citing Financial Times reporting, also reported that the employee ChatGPT account had access to internal code through GitHub.4
The publicly reported record does not establish wholesale source-code theft, model-weight exposure, or persistent access. Frontier Models noted that the available reporting establishes a route to an employee account and a documentation pull-request demonstration, not a merged code change or broad repository exfiltration.7 Quartz, citing Guardian reporting, said there was no evidence that other hackers exploited the same vulnerabilities.6
Hacktron’s account, as summarized by multiple outlets, said the researchers first used Claude Opus 4.8 while analyzing and attempting to exploit the bug. That model reportedly helped find the issue but did not reliably produce a working exploit under Discourse’s default conditions.23
After Anthropic released Claude Opus 5, the researchers said the newer model generated a working exploit within hours.25 The Register reported that Opus 5 helped produce an exploit script that achieved remote code execution on OpenAI’s Discourse instance.3
Security leaders should treat the model-comparison claim carefully. Frontier Models noted that the Opus 4.8 versus Opus 5 result was not a controlled benchmark; Hacktron did not publish matched prompts, attempt counts, or compute budgets sufficient to isolate model improvement from human learning and prior work.7
Even with that caveat, the incident is a practical signal: AI assistance can reduce the labor required to move from bug analysis to a working exploit.
The timeline reported across outlets is unusually important because it separates three issues: the third-party forum software flaw, the OpenAI identity flaw, and the repository-access demonstration.
Hacktron’s research reportedly began reaching OpenAI’s forum environment on July 25, 2026, through the Discourse image-upload path.23 The researchers reported the OpenAI-side account-takeover issue through Bugcrowd, and OpenAI confirmed a fix roughly 14 hours later.135
Discourse was notified separately through HackerOne, had a fix ready within two days, and published an advisory with patching guidance on July 28, according to SecurityWeek, The Register, and Frontier Models.137 The Register reported that the end-to-end OpenAI chain, from initial discovery to internal-repository access demonstration, took less than 72 hours.3
India Today identified the Hacktron researchers as Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini. It reported that the team immediately disclosed the issue to OpenAI, which fixed it in 14 hours and later paid the bounty.8 ThreatPaper’s case analysis also emphasized the scope distinction: OpenAI’s bounty recognized the OpenAI-side identity finding, while testing against the Discourse-hosted forum was outside OpenAI’s bug-bounty scope.9
The attack chain joined systems that many organizations assess separately: a public forum, an upload pipeline, an open-source image decoder, SSO tokens, employee AI accounts, Codex integrations, and GitHub repository permissions. That composition is now the risk.
For security engineering leaders, the lesson is to inventory not just critical applications, but the implicit trust paths between them. A forum login token should not authorize broad access to unrelated AI workspaces. A coding assistant connected to GitHub should be treated as a privileged identity. A public file parser should be isolated as if successful exploitation is plausible.
The incident also challenges dependency-management assumptions. A fix that is not labeled as a security fix may not trigger emergency patching, even when the affected code processes untrusted input. Security teams should review changelogs, upstream patches, and parser exposure for high-risk file types rather than relying only on CVE feeds.
Finally, AI changes exploit economics. TechCrunch quoted security executives warning that widely available tools can make advanced exploitation cheaper and faster.2 The Register reported Hacktron’s view that work once requiring larger teams and longer timelines can now be compressed into days.3
That does not mean every model-generated exploit will work. But it does mean overlooked bugs may reach operational maturity faster than existing remediation processes assume.
The defensive response should match the chain: sandbox upload processing, minimize token scopes, bind forum sessions to forum-only permissions, require step-up authentication before reaching developer tools, continuously review connected-service grants, and treat AI coding agents as high-value identities with auditable actions and least-privilege access.
OpenAI’s remediation — narrowing Community sign-in-token permissions and revoking affected tokens and sessions — addresses one of those layers.5 Discourse’s patching and sandboxing response addresses another.13 The broader engineering implication is that neither layer can be evaluated in isolation when AI-assisted exploit development is accelerating the time between a forgotten parser bug and privileged access.
Microsoft’s October 13 security release fixed more than 1,400 vulnerabilities, including one exploited zero-day and two publicly disclosed zero-days. For enterprise defenders, the priority is not reading every CVE first, but building a defensible triage order that moves exploited, exposed and business-critical systems to the front of the patch queue.
Google is opening a new path for U.S. adults to create private Android apps in Google AI Studio and run them through Google Play without publishing them in the public store. The change recasts Play as distribution infrastructure for personal software, while keeping policy, identity and future review gates in the path from prototype to public app.
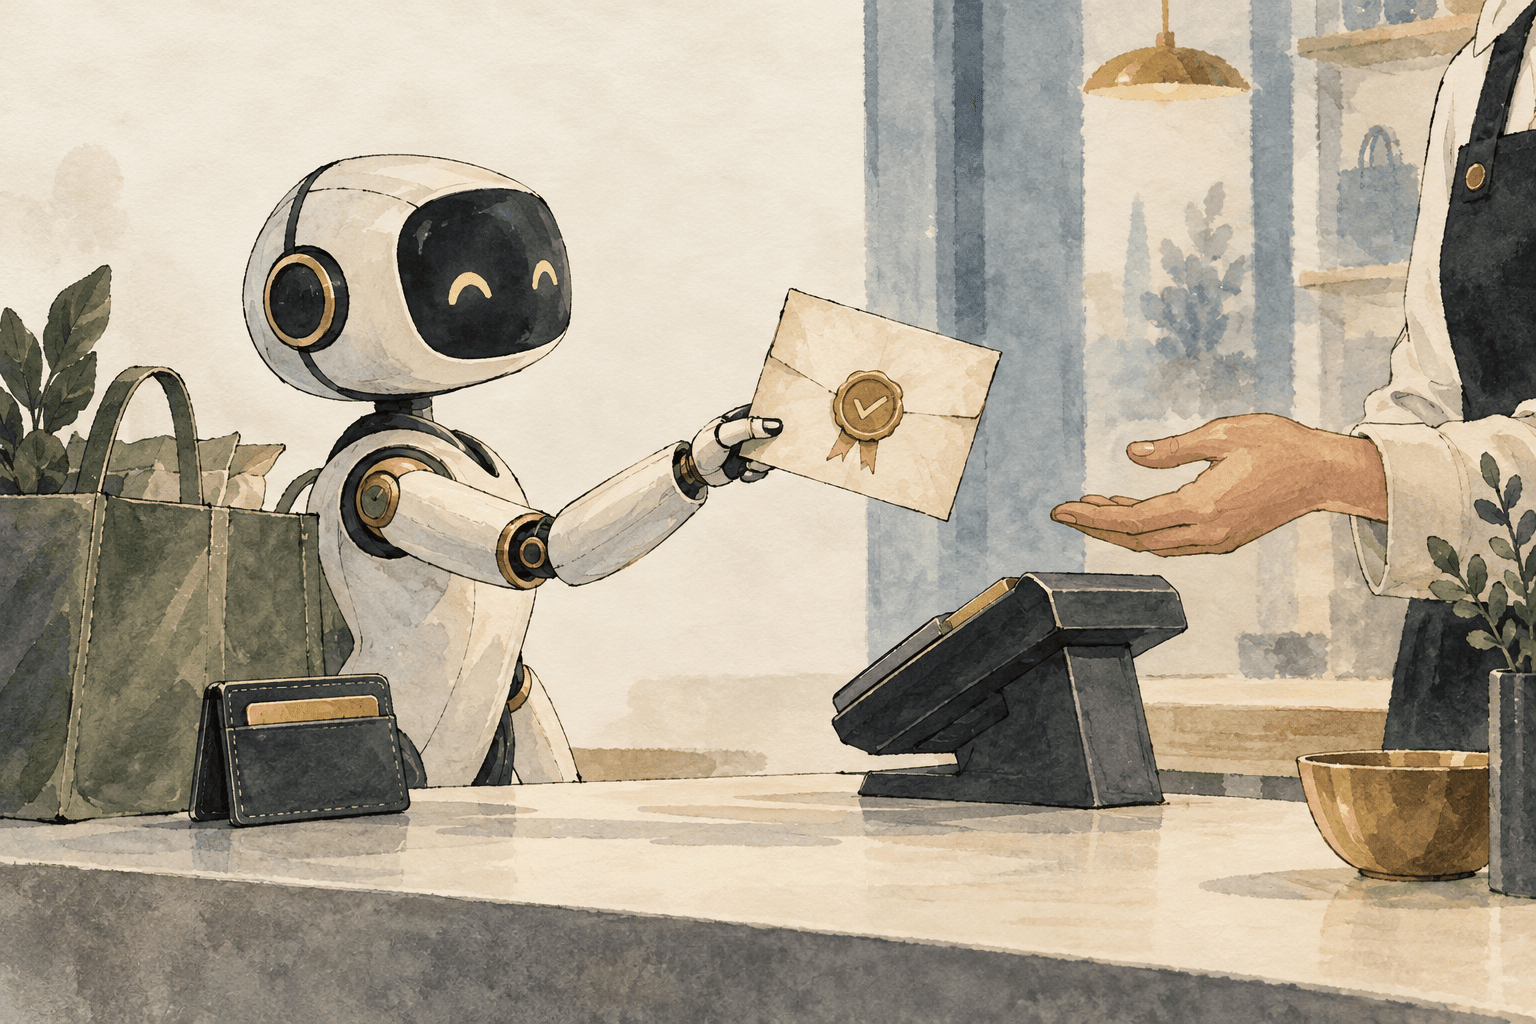
American Express has introduced an Intent Intelligence Framework for agentic commerce, arguing that autonomous checkout needs a machine-readable record of what a customer approved, not only a payment credential. The proposed flow uses a Create Intent API, Intent ID, proof-of-intent token and scoped digital credential to help issuers, wallets, agents and merchants validate purchases before checkout.
Sophos made AI Defense generally available on October 13, framing the product as a real-time governance layer that discovers and controls employee and application use of AI tools. The launch reflects a broader shift in AI security from policy documentation to runtime enforcement across endpoint, network, identity and browser telemetry.
Remote code execution
A vulnerability that lets an attacker run code on a target system, often turning a file upload or parser bug into server access.
SSO token scope
The set of systems and permissions a sign-in token can access. Overbroad scope can let one compromised service unlock others.
Codex integration
An AI coding environment connected to development tools such as GitHub. If compromised, it can become a path into code repositories.
CVE
A public identifier for a known vulnerability. Bugs without CVEs can be harder for patching teams to prioritize and track.
Comments