Microsoft’s Record Patch Tuesday Forces Security Teams to Prioritize Fast
BleepingComputer
news
Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days
Tenable
other
Microsoft’s October 2026 Patch Tuesday addresses 1407 CVEs (CVE-2026-96951)
CrowdStrike
other
October 2026 Patch Tuesday: 1,413 CVEs Include Three Zero-Days and 75 Critical Vulnerabilities
1,400+ flaws
Microsoft’s October 13 release addressed more than 1,400 vulnerabilities by multiple industry counts.
One exploited
CVE-2026-96951, a Windows Shell security feature bypass, was reported as exploited in the wild.
Triage first
Enterprise teams should prioritize exploitation, exposure and business impact over CVE volume alone.
Microsoft’s October 13 Patch Tuesday is less a conventional patch cycle than an operational sorting problem for security teams. The release addressed more than 1,400 vulnerabilities across Windows and other Microsoft products, including one actively exploited zero-day and two publicly disclosed zero-days, according to BleepingComputer and vulnerability-management analyses.12
The immediate task for defenders is clear: identify the small subset of flaws that could create near-term compromise risk, patch or mitigate those first, and avoid letting the size of the release stall remediation. BleepingComputer counted 1,411 flaws in the October release, while Tenable counted 1,407 CVEs and CrowdStrike counted 1,413, reflecting different counting methods and inclusion rules.123 The operational conclusion is the same across sources: this is a record-scale or near-record-scale Microsoft patch event, and vulnerability teams need a prioritization model, not a flat list.
The top priority is CVE-2026-96951, a Windows Shell security feature bypass vulnerability that Microsoft reported as exploited in the wild.126 Tenable said the flaw carries a CVSSv3 score of 8.8 and can be exploited through social engineering, such as convincing a target to open a malicious file, allowing attackers to bypass Mark of the Web protections.2 CIRCL’s Vulnerability-Lookup record also shows CVE-2026-96951 as a Windows Shell command-injection issue affecting Microsoft Windows and identifies it as a CISA Known Exploited Vulnerability added on October 13, 2026.9
That combination — active exploitation, Windows reach, user-assisted delivery and a security-control bypass — should put CVE-2026-96951 in the emergency lane for most enterprises. Endpoint fleets, virtual desktop infrastructure, shared workstations and systems used by highly targeted employees should be checked first for update applicability and deployment status.
The next lane should include the two publicly disclosed zero-days. BleepingComputer identified CVE-2026-108398, a .NET Framework security feature bypass vulnerability, and CVE-2026-92707, a MessagePack-CSharp denial-of-service vulnerability, as publicly disclosed before patch availability.1 Tenable said CVE-2026-108398 could allow an attacker to bypass Windows Defender Application Control by registering a malicious .NET assembly to be loaded by a protected process.2 That matters especially in environments that rely on application control as a compensating control for high-risk endpoints, kiosks, administrative workstations or restricted server roles.
The October release is unusually large by any count. BleepingComputer reported 677 elevation-of-privilege vulnerabilities, 317 remote-code-execution vulnerabilities and 254 information-disclosure vulnerabilities, among other categories.1 CrowdStrike reported a similar distribution, with 677 elevation-of-privilege patches, 317 remote-code-execution patches and 254 information-disclosure patches.3 Tenable said elevation-of-privilege issues represented 47.9% of the vulnerabilities it tracked, followed by remote-code-execution flaws at 22.3%.2
But severity and volume alone should not determine sequencing. A critical remote-code-execution flaw in a product not deployed in the environment is less urgent than an “important” flaw already exploited against a broadly deployed Windows component. Security operations teams should rank vulnerabilities using four questions:
That approach turns a release of more than 1,400 items into a smaller set of remediation workstreams.
Tenable’s product breakdown is useful for building those workstreams. Its analysis said the October release included patches for 301 products and components, with Microsoft Office Excel, DNS Server, Windows Kernel, Windows Installer, Windows Win32 Kernel Subsystem, SharePoint, Windows Search, NTFS, .NET, Word, SQL Server and Windows Error Reporting among the largest affected groups.2
For enterprise teams, triage should not stop at Windows desktop patching. The affected surface spans productivity software, identity-adjacent infrastructure, collaboration systems, databases, developer tooling, cloud services and endpoint protection categories. MS-ISAC listed Windows, Office, SharePoint Server, SQL Server, Exchange Server, Developer Tools, Azure, Defender and Edge among affected systems.6
A practical patch order should separate assets into operational cohorts:
BleepingComputer reported that Microsoft introduced an experimental “risk cohorts” approach for the October release, grouping related vulnerabilities to help organizations understand where the largest concentrations of risk sit.1 The reported cohorts included Windows filesystems, storage and backup; Office documents and mail clients; Windows graphics, media and content processing; Windows core and kernel privilege boundaries; and Windows installation, deployment and update services.1
For defenders, cohorts are most useful as a scoping tool, not a replacement for exploit intelligence. They can help assign work to endpoint, server, messaging, infrastructure and application owners, but exploitation status should remain the first filter. A sensible workflow is to map Microsoft’s cohorts against the asset inventory, then overlay known exploitation, public disclosure, internet exposure, business criticality and patch availability.
The first 24 to 72 hours should focus on measurable risk reduction. Teams should confirm whether CVE-2026-96951 is applicable across Windows fleets, deploy available cumulative updates to the highest-risk endpoints and servers, and verify installation through endpoint management or vulnerability scanning. Because the flaw involves Windows Shell and Mark of the Web bypass behavior, defenders should also review recent alerts involving suspicious downloaded files, archive extraction, script execution, shortcut files and user-launched content from email or messaging channels.
Next, teams should identify where .NET Framework, MessagePack-CSharp, Exchange, SharePoint, DNS Server, SQL Server and Active Directory components are present. Tenable highlighted additional notable issues, including Active Directory Domain Services remote code execution and Exchange Server vulnerabilities assessed as more likely to be exploited.2 Those systems should be patched according to exposure and criticality, with change windows compressed for internet-facing or privileged infrastructure.
Finally, organizations should treat end-of-support systems as a separate risk register item. Tenable noted that October 13, 2026 marked the end of the final Extended Security Updates year for Windows Server 2012 and Windows Server 2012 R2, while Windows 10 Enterprise 2016 LTSB and Windows 10 IoT Enterprise LTSB 2016 also reached the end of extended support.2 BleepingComputer also reported end-of-update milestones for certain Windows 11 and Windows 10 editions.1 Assets that cannot receive future security updates should be isolated, upgraded or retired. Otherwise, each Patch Tuesday will widen the gap between known risk and patchable risk.
October’s Microsoft release shows why modern patch management is now an exposure-management discipline. The defenders who move fastest will not be the teams that read every CVE first. They will be the teams that can combine exploit status, asset inventory, business criticality, exposure paths and deployment telemetry into a short, defensible priority queue.
In this release, that queue starts with CVE-2026-96951, expands to the publicly disclosed zero-days, then moves through critical and “exploitation more likely” flaws affecting deployed Microsoft products. Everything else still needs remediation, but not everything needs the same clock.
Google is opening a new path for U.S. adults to create private Android apps in Google AI Studio and run them through Google Play without publishing them in the public store. The change recasts Play as distribution infrastructure for personal software, while keeping policy, identity and future review gates in the path from prototype to public app.
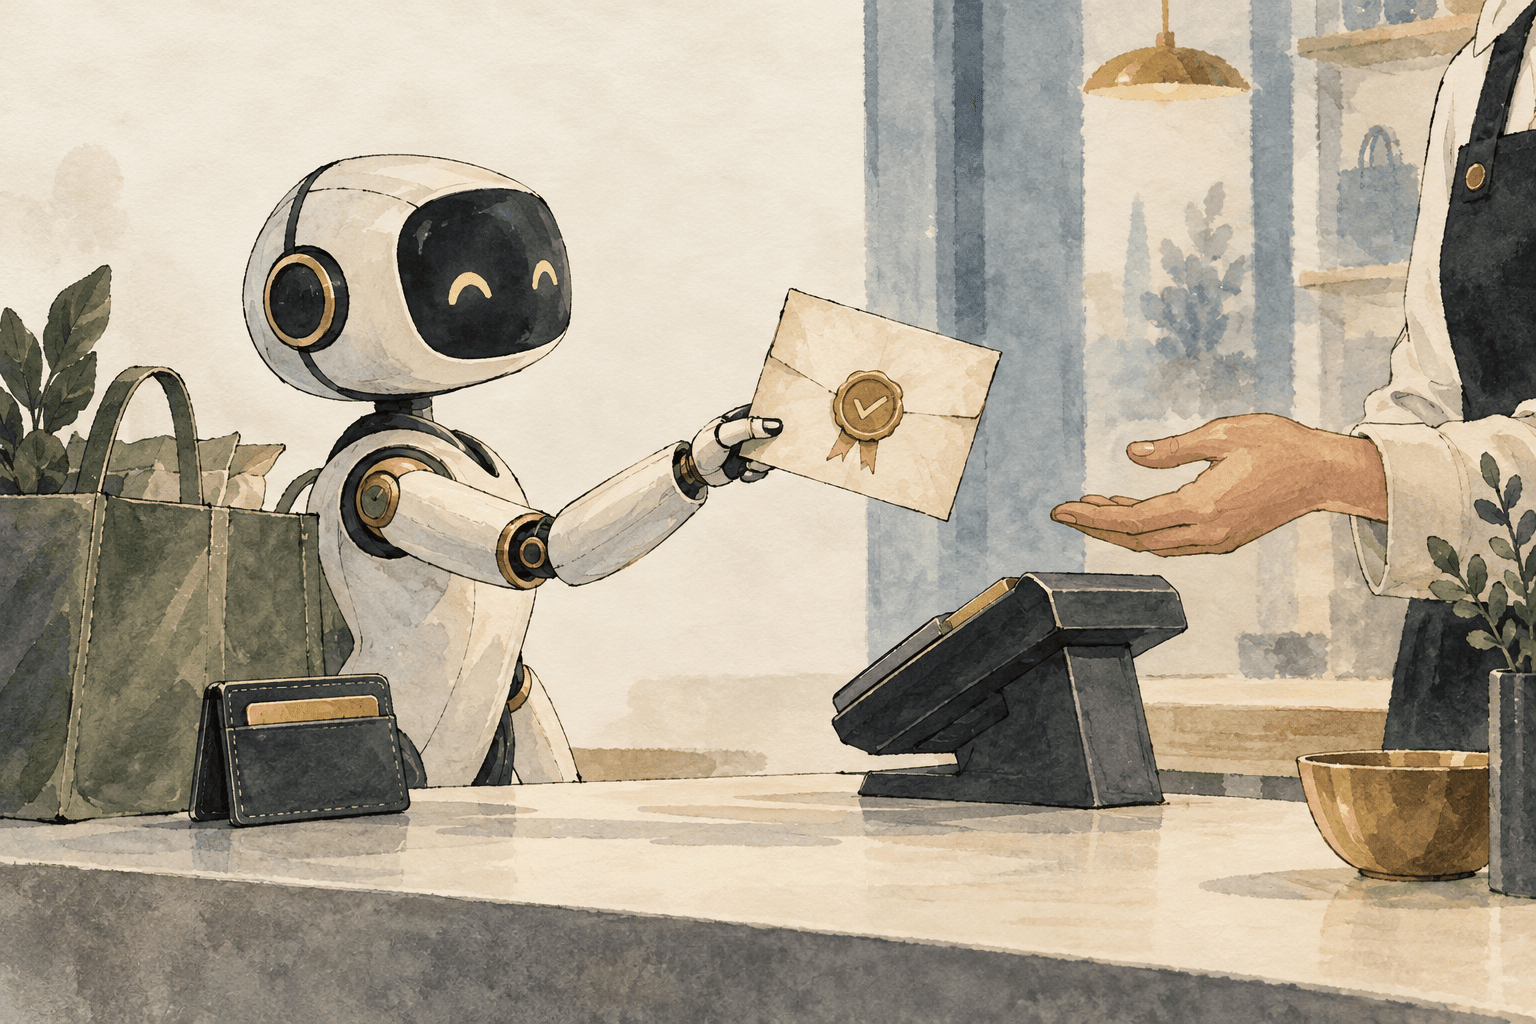
American Express has introduced an Intent Intelligence Framework for agentic commerce, arguing that autonomous checkout needs a machine-readable record of what a customer approved, not only a payment credential. The proposed flow uses a Create Intent API, Intent ID, proof-of-intent token and scoped digital credential to help issuers, wallets, agents and merchants validate purchases before checkout.
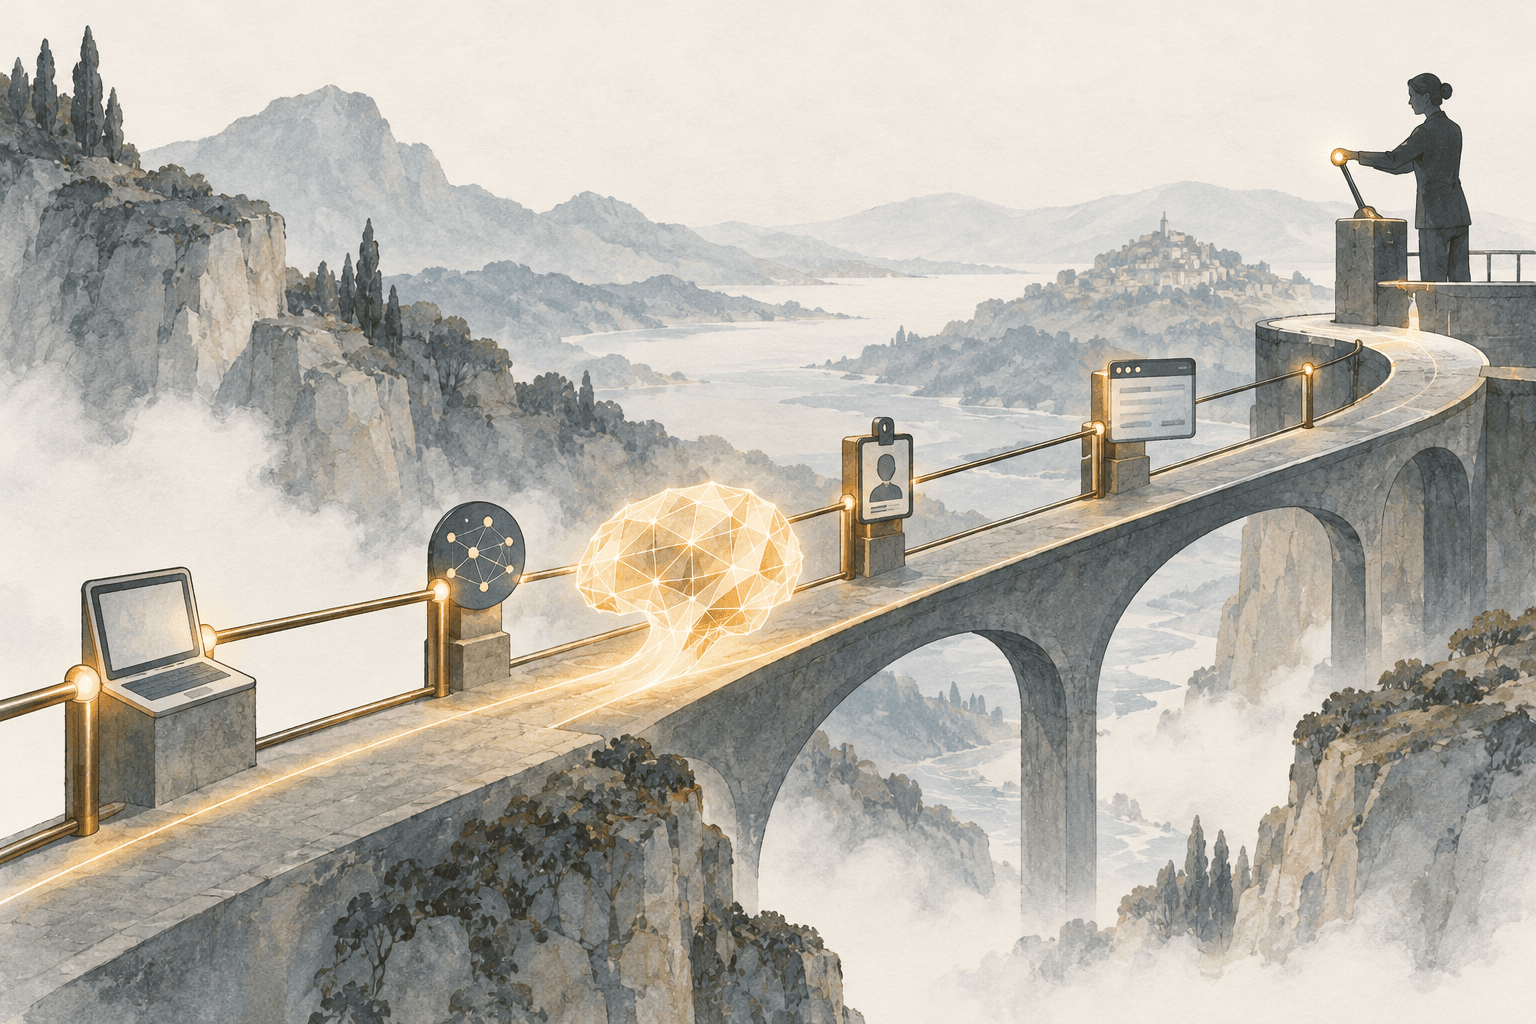
Sophos made AI Defense generally available on October 13, framing the product as a real-time governance layer that discovers and controls employee and application use of AI tools. The launch reflects a broader shift in AI security from policy documentation to runtime enforcement across endpoint, network, identity and browser telemetry.
Workday said its Trusted Agent Platform is now headless, giving customer- and partner-built AI agents governed access to HR and finance data and actions. The move reflects a broader enterprise shift from chat-based assistants toward agents that can operate inside systems of record under permissions, approvals and audit controls.
Zero-day
A vulnerability that was publicly disclosed or exploited before an official fix was available.
Mark of the Web
A Windows security marker applied to files from the internet that helps trigger additional protections when users open them.
Known Exploited Vulnerabilities catalog
CISA’s list of vulnerabilities confirmed to have been exploited, often used by defenders to prioritize remediation.
Risk cohort
A grouping of related vulnerabilities intended to help teams understand and organize patching work by affected technology area.
Comments