Cisco expands Splunk’s agentic SOC into security workflows
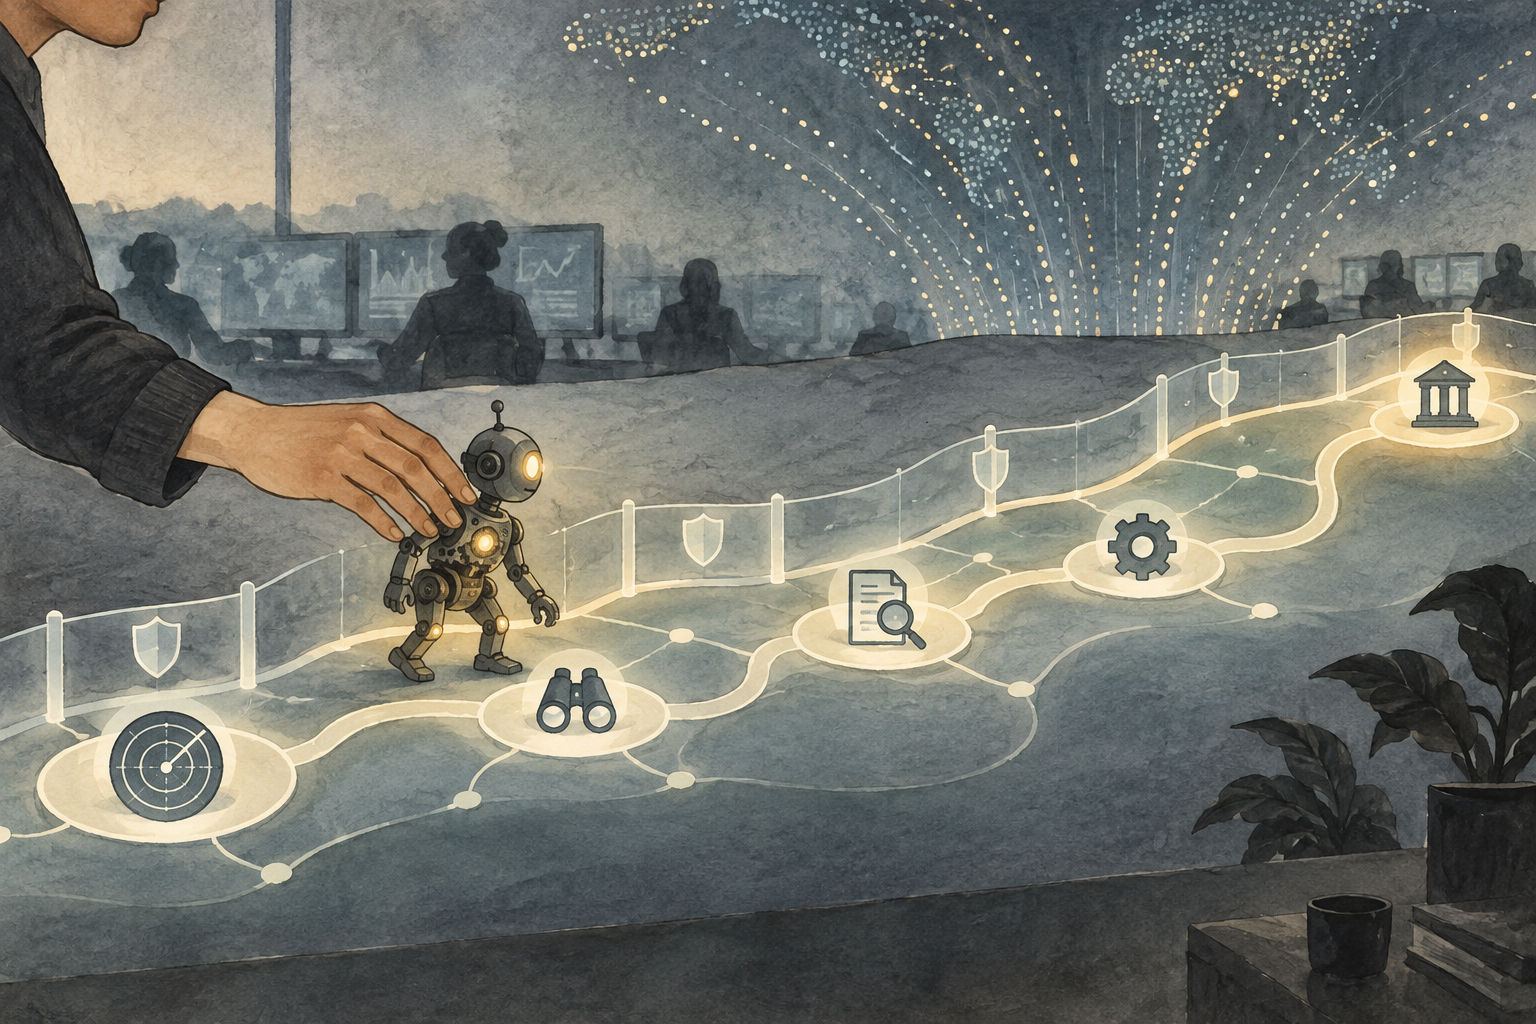
Agentic SOC
Cisco expanded Splunk’s Agentic SOC Workforce across detection engineering, threat hunting, investigation, response and policy governance.
Telemetry Layer
Splunk is using enterprise-wide telemetry from network, cloud, application and identity environments to give agents context for prioritization and remediation.
Human Control
Cisco is emphasizing approvals, auditability, policy governance and analyst oversight rather than positioning the system as fully autonomous defense.
Cisco is expanding Splunk’s agentic security operations capabilities with new AI agents designed to help SOC teams build detections, hunt threats, investigate incidents, coordinate response and enforce policy governance, the company announced around .conf26.1
The update moves Splunk beyond AI features that summarize alerts or draft analyst notes and into the allocation and execution of SOC work. Cisco said the expanded Agentic SOC Workforce combines enterprise-wide telemetry with specialized AI agents powered by frontier and domain-specific models. The agents use signals from network, cloud, application and identity environments to produce explainable verdicts and prioritize remediation.1
For security operations leaders, the significance is not that Splunk is promising a fully autonomous SOC. It is that Cisco is embedding AI agents into the operational fabric of security work. The company’s framing emphasizes human governance, auditability and analyst control, including approvals and policy controls, as agents take on more steps in detection, triage and response workflows.1
Splunk’s Agentic SOC Workforce is being extended across four operational areas: detection and security engineering, threat hunting, investigation and response, and governance and policy. Splunk says the agents are designed to operate inside existing SOC processes, helping analysts and engineers move faster while maintaining human control.7
That marks a shift in how security vendors are packaging AI. Earlier generative AI features in SOC tools often centered on summarizing incidents, translating queries or helping analysts use natural-language search. Cisco’s new Splunk capabilities aim to assign specialized AI agents to discrete SOC functions, including tuning detections, surfacing emerging threats, accelerating triage, recommending containment and keeping actions aligned with standard operating procedures.2
The company also said Splunk Enterprise Security Essentials will gain new agentic security operations capabilities, while Splunk Enterprise Security Premier will add deeper agentic autonomy and the broader Enterprise Security feature set.1 That packaging suggests Cisco is trying to make agentic SOC functions available to more teams while reserving more advanced autonomy for higher-tier deployments.
Cisco’s approach depends heavily on Splunk’s role as a machine data platform. The company said the agents correlate full-stack telemetry across network, cloud, application and identity sources to reduce alert noise and accelerate mean time to remediate.1
The telemetry layer matters because agentic security tools are only as useful as the data and context they can reason over. Splunk’s updated Exposure Analytics is designed to broaden asset coverage, preserve historical change context and apply business-specific risk insights. The goal is to help agents and analysts prioritize exposures that are active, critical or tied to sensitive business services.1
Splunk’s security blog also described more than 1,300 security integrations and closer integration with the Cisco Security portfolio, including signals from network, firewall, identity, cloud and endpoint controls.7 The intended result is a SOC workflow in which an agent can move from signal to context to recommended action without forcing analysts to stitch together evidence from multiple tools manually.
Cisco is not presenting the new Splunk capabilities as unchecked machine control. The company’s announcement repeatedly ties agentic SOC functions to explainability, governance and analyst oversight.1
That distinction matters as SOC leaders evaluate where automation should stop. Agents may be able to enrich alerts, recommend containment or identify policy gaps, but response decisions often carry business risk. Isolating a host, blocking traffic, disabling an account or changing policy can disrupt operations if the system is wrong.
Cisco’s implementation still has to prove where automation ends and analyst judgment begins. The practical test for customers will be whether Splunk can make approval points, audit trails and policy constraints visible enough for SOC managers to trust the workflow under pressure.
Industry coverage framed the same issue as a broader control problem. CX Today noted that AI-driven attacks, cloud identity risk and data sovereignty are making control over data, identity and AI agents a central cybersecurity battleground.3 In that context, monitoring the behavior of defensive AI agents becomes part of the SOC’s own risk management process, not just a productivity feature.
Cisco also announced broader Splunk AI observability updates, including Tokenomics capabilities in Splunk Agent Observability to track AI token spending and coding-agent usage in real time.1 Enterprise AI World reported that Splunk Agent Observability evaluates agent and model behavior, observes performance across the AI stack and applies runtime guardrails intended to block inaccurate or unsafe actions, including hallucinations or sensitive data leakage.2
Those controls are relevant to security leaders because agentic SOC tooling creates a new class of operational dependency. SOC teams will need to know not only whether an endpoint, identity provider or cloud control is behaving abnormally, but also whether the AI agent interpreting those signals is reliable, within budget and operating inside policy.
Cyber Risk Leaders described the update as part of a broader Cisco push to give teams visibility into AI agent performance and spending, alongside the Splunk security updates.6 eeNews Europe similarly highlighted guardrails around agent behavior and the expansion of Splunk’s Agentic SOC Workforce for detection, hunting, investigation, response and governance.4
The security announcement also sits inside a larger Splunk AI infrastructure update. Cisco said Cisco AI POD for Splunk is available for on-premises customers as part of Cisco Secure AI Factory with NVIDIA, bringing Splunk AI workloads to on-premises, private cloud and air-gapped environments.1
That matters for regulated industries, public-sector organizations and critical infrastructure operators that cannot move sensitive telemetry into public cloud services for analysis. Enterprise AI World reported that Splunk AI Assistant is available on the layer now, while Agent Launchpad is expected later this year for ad hoc agentic investigations and custom agent building.2
The on-premises option may help Cisco answer one of the central objections to AI-enabled SOC modernization: whether sensitive security data can remain under customer control. eeNews Europe reported that the Cisco-NVIDIA work is intended to support on-premises and air-gapped deployment, alongside model and agent guardrails.4
The near-term question is how these agents perform in production SOC environments rather than controlled demonstrations. MSSP Alert described Cisco’s positioning as a shift from manual workflows toward an agentic operating model. But managed service providers and enterprise SOCs will still need evidence on false positives, escalation quality, auditability and workflow disruption.5
Three implementation details will likely determine adoption. First, SOC leaders will need clear approval boundaries for high-impact actions. Second, they will need measurable improvements in mean time to detect, investigate and remediate without simply moving the review burden to another queue. Third, they will need governance reporting that shows which agent made a recommendation, what data it used and which human approved or rejected the action.
Cisco’s Splunk announcement shows agentic security tooling expanding from alert assistance into SOC work orchestration. The harder phase now begins: proving that machine-speed workflows can remain accountable to human operators, business risk and policy constraints.

Anthropic’s new financial-advisor product puts Claude inside wealth-management workflows while leaving sensitive client records in partner systems. The launch is an early test of whether MCP-style connectors, enterprise controls and human approval can make vertical AI agents viable in regulated industries.

NIST IR 8587 shifts token theft prevention from post-breach cleanup to design-time controls for SSO, federation, API access and workload identity. For cloud security teams, the practical mandate is to protect signing keys, shorten credential lifetimes, validate every token path and monitor lifecycle events across providers and customers.

Stanford-led researchers say Paper2Agent can convert scientific papers, code and data into AI agents that answer questions, reproduce analyses and collaborate with other paper agents. The larger claim is infrastructural: papers could become executable, attributable research objects, but the system still depends on usable code, author-supplied context and human oversight.

Google’s Gemini 3.8 Live and Gemini 3.8 Live Extended Thinking move real-time voice agents beyond turn-taking conversations. For developers, the important change is architectural: applications now need to track session state, asynchronous tools, latency budgets and failure modes while speech continues.
Agentic SOC
A security operations model in which AI agents perform or assist with SOC tasks such as triage, investigation, detection tuning and response recommendations.
Telemetry
Machine data from systems such as networks, cloud services, applications, identities and endpoints that security tools analyze for signs of risk or compromise.
Human-in-the-loop
An operating model where AI can recommend or prepare actions, but humans review, approve or override important decisions.
Tokenomics
The tracking and management of AI token consumption and related costs across models, agents and users.
Comments