Apple’s Full Disk Access changes show AI agents are becoming an OS security problem
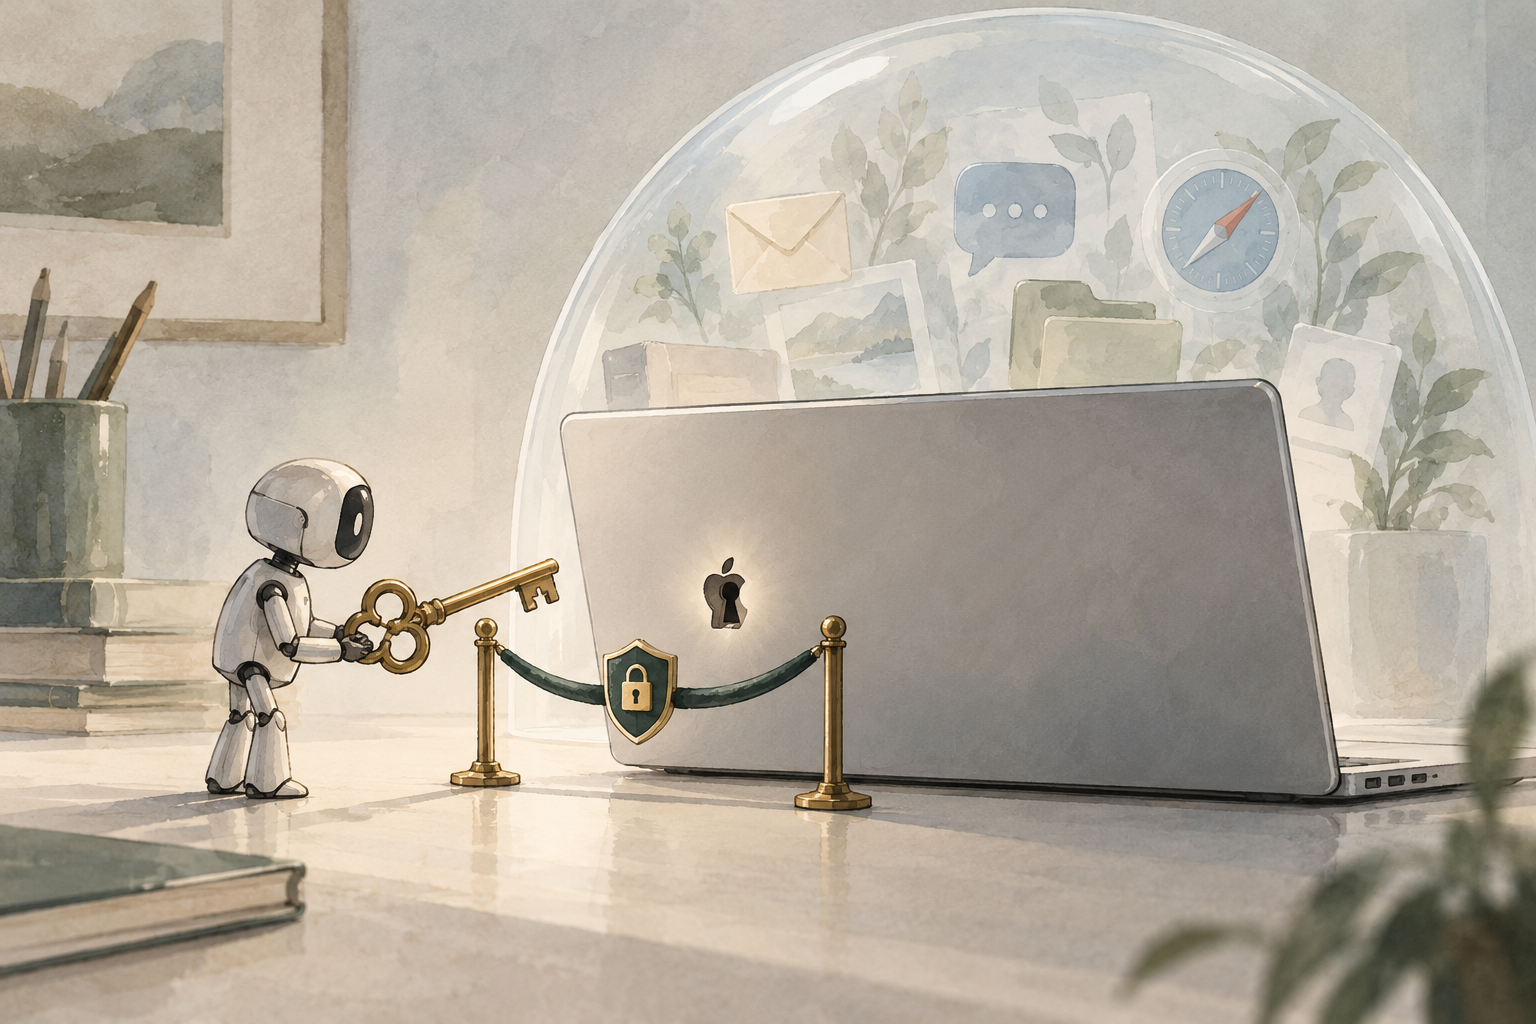
Apple tightens access
Apple said macOS Full Disk Access will get additional controls because AI agents increase the risk of broad local data exposure.
Agents raise stakes
Desktop AI agents can combine files, mail, messages and browser data into a single operating context, making legacy permissions more sensitive.
Auditability gap
Security teams may need logs, scope controls and just-in-time access models to verify what agentic apps actually read and do.
Apple said it will add new controls around macOS Full Disk Access, warning that increasingly capable AI agents make broad local permissions more dangerous because they can expose files, mail, messages and browsing history without users fully understanding the scope of access.1
The announcement, published October 2, 2026, is an early platform response to a security pattern operating-system vendors can no longer ignore: desktop AI agents often need deep local context to be useful, but legacy permission systems were not designed for autonomous software that can continuously read, reason over and act on a user’s private workspace.
For security and platform engineering leaders, the significance is less about one macOS setting than a broader boundary shift. A permission originally meant to help backup and maintenance tools function is becoming a front-line control for agentic applications. Apple said Full Disk Access can largely bypass protections designed to protect private data, and that future grants of this “extraordinary” access should require very explicit user action.1
The company did not specify when the new controls will arrive or exactly how they will work.4 But the direction is clear: operating systems are beginning to treat agent access to local data as a distinct security and consent problem, not just another app-permission prompt.
Full Disk Access is powerful because it can give a macOS app access far beyond a single file picker, folder grant or application-specific data store. Apple said the setting exists largely so backup apps can function properly, but warned that some developers are using it in ways that can put users at risk.1
That risk profile changes when the app is an AI agent. A conventional utility may read broad areas of a disk to index, back up or clean files. An agent may do something more expansive: synthesize information across messages, mail, browser state and local documents; trigger workflows; maintain memory; and respond proactively. In other words, the permission is not just read access. It becomes context access.
Recent reports linked Apple’s announcement to concerns around Meta’s Muse app, including a columnist’s claim that the app appeared to know the contents of private messages, a claim Meta disputed.2 Ars Technica reported that Meta’s position was that Muse required both macOS Full Disk Access and an enabled Messages connector to read Messages content. macOS security researcher Patrick Wardle argued that Full Disk Access is technically broad enough to read many non-root local files, including chats, browsing data and cookies.3
Apple did not name Meta, Muse or any other developer in its announcement.3 Still, the timing placed the company’s developer notice inside a wider debate over whether users can reasonably understand what they are granting when an always-on assistant asks for operating-system-level access.
Apple’s language points to a gap between formal consent and meaningful user understanding. The company said users who genuinely want to grant an app such access should be able to do so only through “very explicit user action,” and that users must clearly understand the risks before granting it.1
That framing matters. Traditional permission prompts often ask whether an app may access a category of data or a device capability. Agentic apps complicate that model because the same permission can support many downstream behaviors: summarizing local files, searching messages, extracting attachments, using browser sessions, or acting on a user’s behalf.
The result is a mismatch between the prompt and the system behavior it enables. A user may believe they are authorizing productivity assistance. The operating system may actually be granting a durable capability to inspect a large portion of the local data estate.
Daring Fireball’s analysis captured the platform contrast: iOS and iPadOS do not offer third-party apps an equivalent path to read protected email or end-to-end encrypted messages simply because a user approves every prompt, while macOS can expose far more of the startup drive when broad permissions are granted.7
For platform teams, that suggests permission dialogs alone are an inadequate control plane for agents. Future designs may need clearer scope, shorter-lived grants, purpose binding, per-data-source controls, and audit trails that show not only what permission was granted, but what the agent accessed and why.
Apple has not said whether its coming changes will include logging, developer attestations, access receipts or new user-visible audit surfaces. But the agentic-app problem naturally pushes platforms in that direction.
If an app with broad access reads a message database, indexes browser history or pulls mail attachments into an embedding store, a one-time prompt is a weak accountability mechanism. Security teams need evidence. Users need intelligible explanations. Enterprise administrators need policy controls that distinguish between backup software, endpoint detection, accessibility tools and AI agents.
This is where desktop operating systems may begin borrowing from cloud security. In cloud environments, high-risk privileges are increasingly paired with just-in-time elevation, session recording, scoped tokens, policy evaluation and logs. Desktop agents create a similar need locally: consent should be narrow enough to express intent, and activity should be observable enough to verify that the agent stayed within that intent.
For enterprises, the issue also intersects with data-loss prevention and insider-risk programs. An agent that can read local messages, documents and browser sessions may become a privileged data broker even if it is not malicious. If compromised, misconfigured or overbroad by design, it can collapse multiple data boundaries at once.
The risk is not limited to intentional overreach by app developers. WIRED reported on a recently patched vulnerability in the ChatGPT macOS app that could have let attackers take over the app on a victim’s computer and reach chat logs, app-stored data and connected browser sessions.6 OpenAI acknowledged the flaw and fix in a September 25 change log, according to the report.6
That incident underscores why operating-system vendors are likely to tighten local agent privileges even when developers act in good faith. Agent apps are valuable targets because users may grant them durable access to personal and corporate context. A compromise of the agent can become a compromise of whatever the agent can reach.
This dynamic changes the threat model for desktop software. The old question was whether an app should be trusted. The agent-era question is whether the operating system can constrain and observe a trusted app after it has been granted a powerful role.
Apple’s challenge is that Full Disk Access is not inherently illegitimate. Backup tools, disk utilities, endpoint security products, developer tools and accessibility software may require broad local privileges to function. MacRumors noted that Apple has not yet said when the new controls will be implemented, leaving open the practical question of how the company will avoid breaking legitimate workflows.4
The risk for platform vendors is overcorrection. If controls are too blunt, they may impair power-user workflows and enterprise management tools. If they are too permissive, agentic apps will continue to stretch legacy permissions into broad surveillance and automation channels.
A likely middle path is differentiated treatment for classes of software. Backup software, endpoint tools and AI agents may all request broad access, but the operating system can require different disclosures, entitlements, review processes, runtime indicators or management policies depending on the declared purpose and observed behavior.
Apple’s statement that AI agents make the risks grow “substantially” suggests the company sees autonomy as a meaningful design factor, not just another app category.1 That is an important precedent for other desktop platforms.
Apple’s move should be read as a signal that broad local permissions are likely to become more regulated by the platform layer. Engineering leaders building agentic desktop apps should expect more explicit consent flows, stronger review of why local data is needed, and potentially more friction around persistent access.
Enterprise security teams should inventory which desktop applications have broad local privileges, including Full Disk Access on macOS, and identify which of those applications are AI-enabled or connected to external model services. They should also review whether current endpoint telemetry can show when an agent reads message stores, mail databases, browser profiles, cookies or local document repositories.
Product teams building agents should assume that “ask for everything once” will become a weaker and riskier design pattern. More sustainable architectures will minimize local reads, request access at the moment of need, explain the purpose in plain language, keep sensitive processing local when possible, and provide logs or user-facing histories of agent actions.
The wider platform lesson is that AI agents turn desktop permissions into active security boundaries. Apple’s Full Disk Access change is early evidence that operating-system vendors will increasingly decide how much autonomy third-party agents can exercise over a user’s local digital life.
That will reshape both app design and enterprise controls. The most successful agent platforms will not be the ones that obtain the broadest permission fastest. They will be the ones that make access constrained, explainable and auditable enough for users and administrators to trust.

Google is positioning Gemini 4 Argon as a frontier model for software engineering, enterprise automation and cyber defense, but it is not releasing the system broadly. Instead, the company is making vetted access, monitoring and security governance part of the product itself.

Circuit Breaker Labs is testing chatbots with AI-generated users that vary by age, language, culture and communication style. The shift points to a new safety benchmark for consumer AI: whether systems can recognize psychological risk as it develops over time, not just refuse a dangerous prompt.

Fortinet says CVE-2026-104286, a critical FortiMail path traversal vulnerability, is being exploited in the wild, and CISA has set an October 4 remediation deadline for federal agencies. Enterprise defenders should treat patching or mitigation as only the first step, then validate exposure, logs, files, indicators of compromise and possible abuse of the email gateway control plane.

Epic has reportedly paused most product development for about six weeks after Anthropic’s Mythos cybersecurity model surfaced MyChart flaws that could risk patient data. The episode shows how frontier cyber models are beginning to force critical software vendors to reorder product roadmaps around accelerated vulnerability discovery.
Full Disk Access
A macOS privacy setting that can allow an app to read broad areas of local storage, originally useful for tools such as backup software.
Agentic app
Software that can pursue tasks with some autonomy, often using local context such as files, messages, calendars or browser state.
Purpose binding
A security design principle in which access is tied to a specific user-approved purpose rather than granted broadly for any future use.
Just-in-time access
A privilege model that grants sensitive access only when needed and often for a limited duration.
Comments